Use case — Agent runtime
Engineers want agents. Security wants control.
One governed place for every agent your team runs. Isolated, fenced, audited, and metered, with the guardrails kept on.
Reply within one business day · priced per org · bring your own keys, never marked up
What is a sanctioned agent runtime?
A sanctioned agent runtime is one managed platform, approved once by Security, where every agent an org runs — OpenClaw, Claude Code, Codex, Hermes, or your own harness — executes in true isolation with strict network access, scoped credentials, a unified audit log, native SSO, human-in-the-loop approvals, and hard cost caps.
Without agen-x
- Fragmented tools: teams use scattered open-source and commercial agents.
- No governance: plaintext tokens on laptops. No audit logs.
- Platform burden: securing one agent yourself takes months. Then the next one arrives.
With agen-x
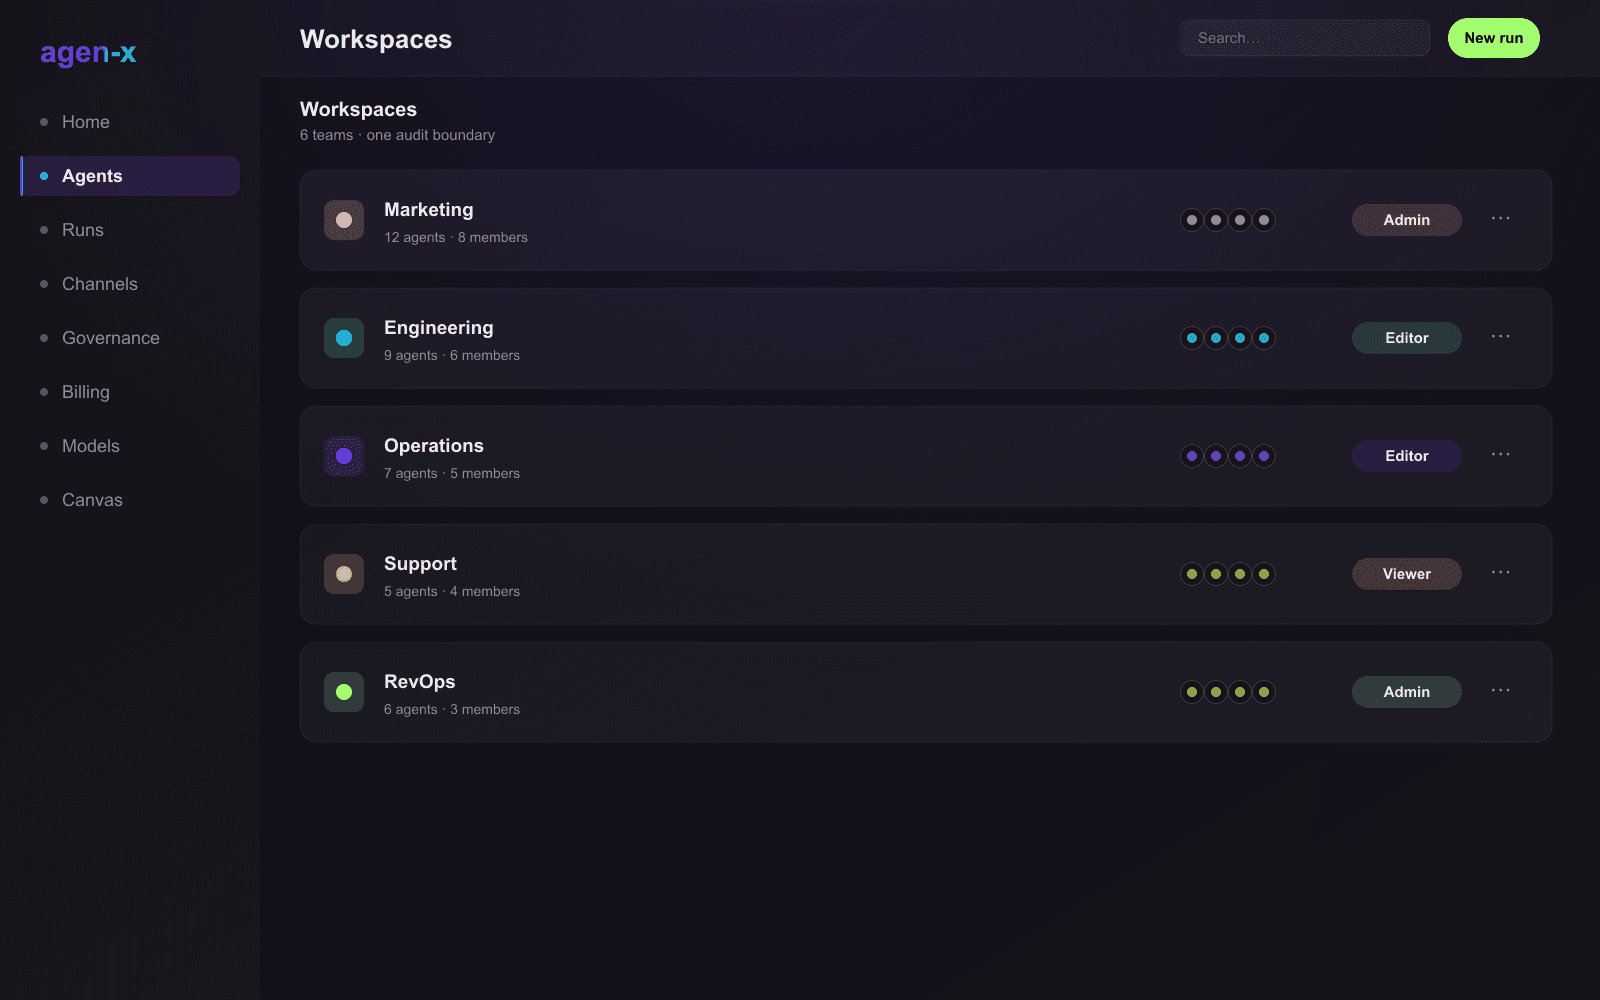
- Secure workspaces: agents run in true isolation with strict network access.
- Unified audit log: Security sees every action across every runtime.
- Human-in-the-loop: irreversible actions wait for explicit approval.
- Cost control: hard caps prevent bill shock.
Security controls, built-in
Verifiable isolation
Security you can test, not just a PDF.
Strict network boundaries
Exfiltration blocked by default.
Scoped credentials
No plaintext leaks.
Native SSO and RBAC
One review for every agent.
Popular sanctioned agents
- An open-source ops agent watching a support queue.
- Claude Code or Codex running 24/7 on a repo.
- An always-on assistant for internal research.
Which agent will you sanction first?
Reply within one business day · priced per org · bring your own keys, never marked up